Web Application Firewalls: What They Can and Cannot Stop
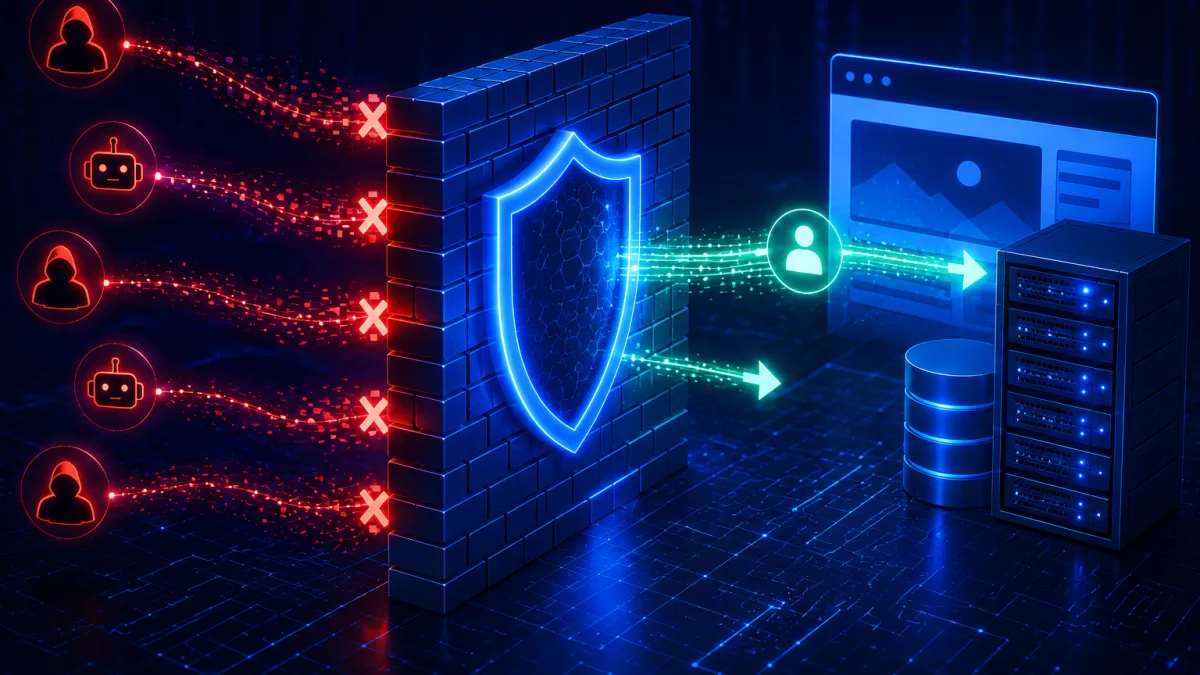
The aim is to connect the technology with everyday operational decisions. A WAF evaluates HTTP requests and can block many malicious patterns before they reach an application.
Updates, news and developments from hosting, security and Internet infrastructure.
The aim is to connect the technology with everyday operational decisions. A WAF evaluates HTTP requests and can block many malicious patterns before they reach an application.
This article is based on a real 2025 incident or official security disclosure. Cloudflare reported blocking 20.5 million DDoS attacks in the first quarter of 2025, a 358% year-over-year increase.
This article is based on a real 2025 incident or official security disclosure. On 9 April 2025 CISA added CVE-2024-53197 and CVE-2024-53150, Linux kernel out-of-bounds vulnerabilities, to its Known Exploited Vulnerabilities…
The aim is to connect the technology with everyday operational decisions. File and directory permissions determine which users and processes may read, modify or execute data.
The aim is to connect the technology with everyday operational decisions. Credential stuffing uses username and password combinations stolen from one service against other services.
The aim is to connect the technology with everyday operational decisions. Passwords remain necessary, but a password alone is a single point of failure.
This article is based on a real 2025 incident or official security disclosure. CISA added CVE-2024-55591 to its Known Exploited Vulnerabilities catalog on 14 January 2025.
Reduced staffing and slower response can make security incidents harder to manage during holiday periods.
A compromise can begin with one vulnerable file and then affect multiple parts of an application.
Automated login attempts continue to target websites, control panels and online accounts every day.
SSL is essential, but it is only one part of protecting a modern website.