CISA Adds Citrix and Git Flaws to KEV: Why Active Exploitation Changes Patch Priority
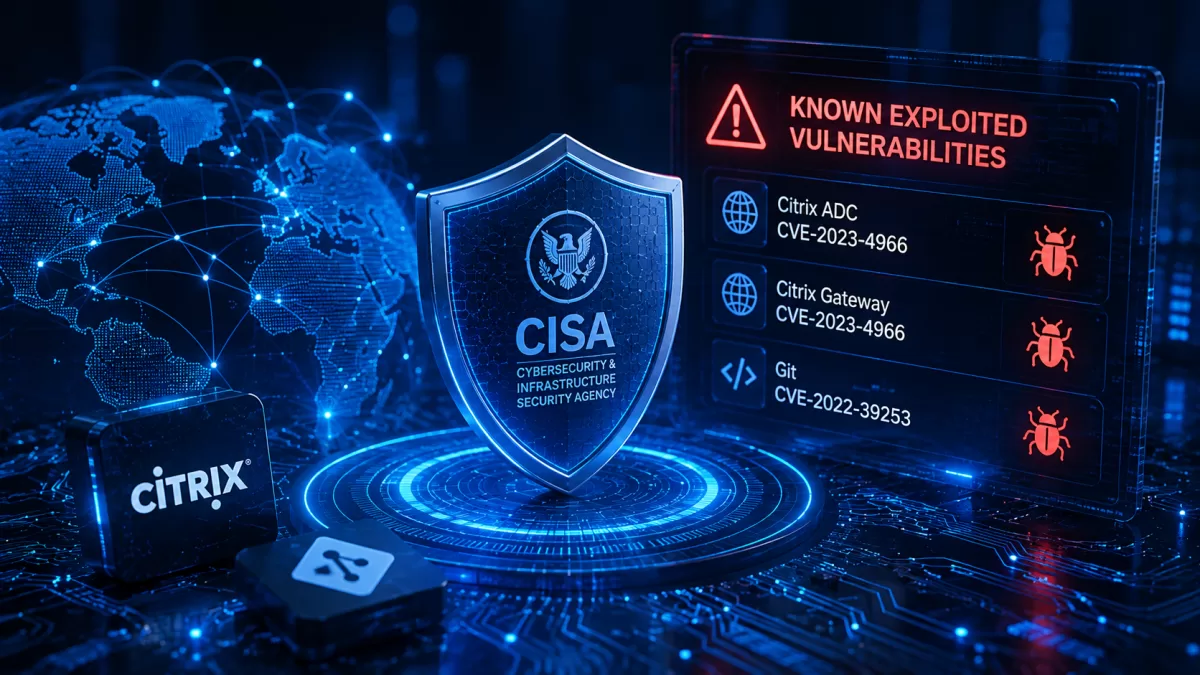
On 25 August 2025 CISA added three vulnerabilities to its Known Exploited Vulnerabilities catalog: two Citrix Session Recording flaws and a Git…
Updates, news and developments from hosting, security and Internet infrastructure.
On 25 August 2025 CISA added three vulnerabilities to its Known Exploited Vulnerabilities catalog: two Citrix Session Recording flaws and a Git…
The aim is to connect the technology with everyday operational decisions. Logs provide a timeline of requests, authentication events, errors and system activity.
The aim is to connect the technology with everyday operational decisions. PHP versions have defined support lifecycles.
This article is based on a real 2025 incident or official security disclosure. On 28 July 2025 CISA added CVE-2025-20281 and CVE-2025-20337 affecting Cisco Identity Services Engine to its Known Exploited Vulnerabilities catalog…
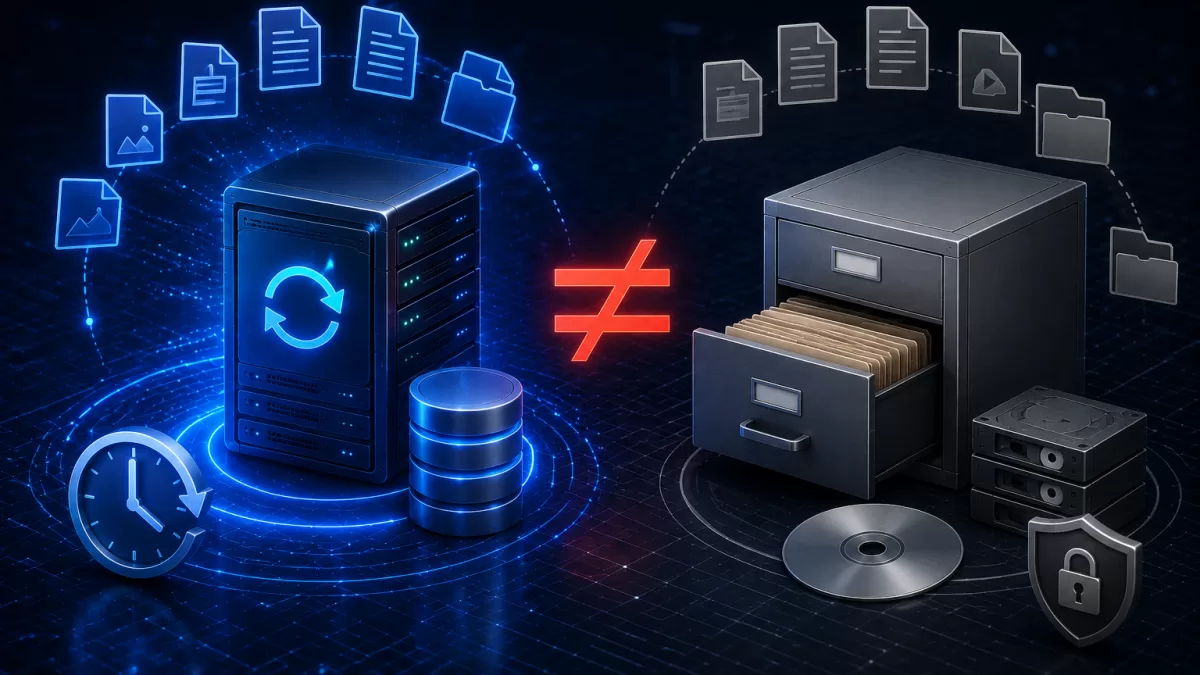
The aim is to connect the technology with everyday operational decisions. Backups are primarily designed to restore systems after deletion, corruption, failure or compromise.
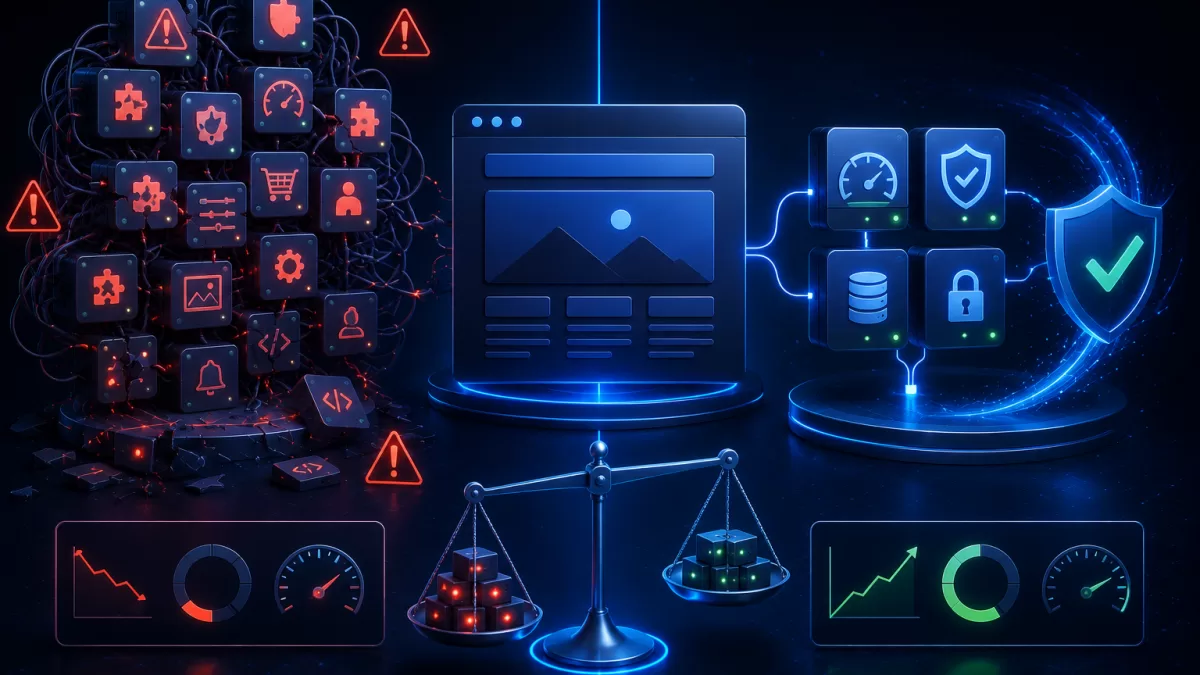
The aim is to connect the technology with everyday operational decisions. The number of installed plugins alone does not determine whether a WordPress site is slow or insecure.
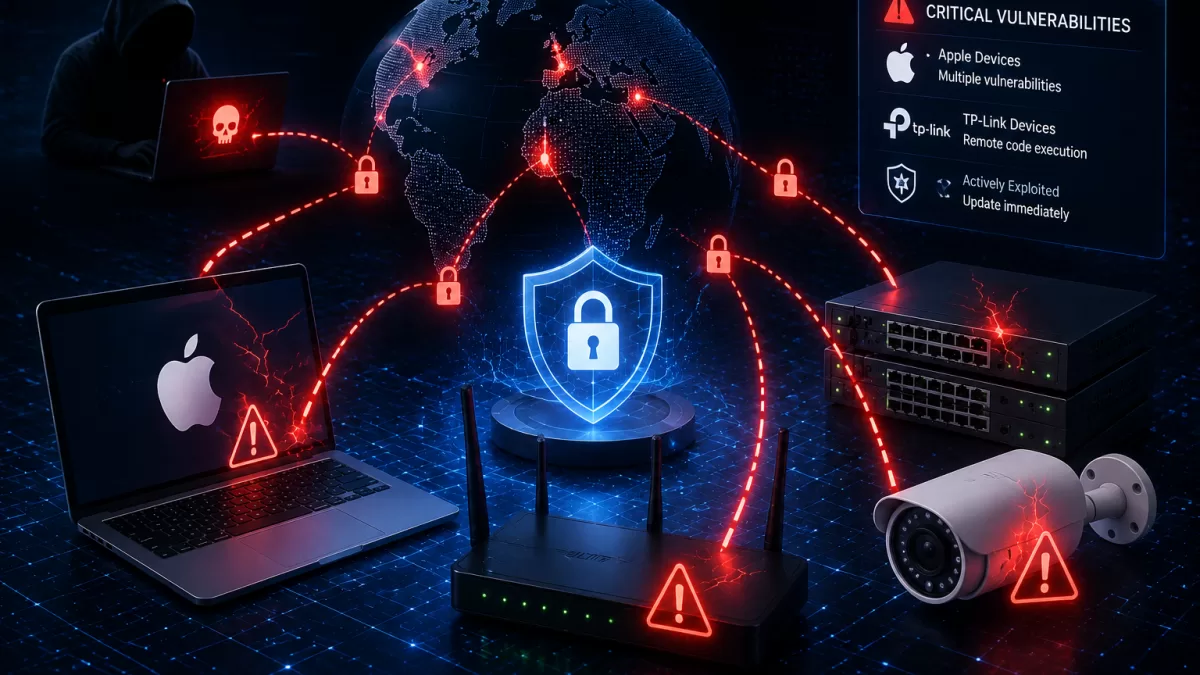
This article is based on a real 2025 incident or official security disclosure. On 16 June 2025 CISA added CVE-2025-43200 affecting multiple Apple products and CVE-2023-33538 affecting TP-Link routers to its Known Exploited…
The aim is to connect the technology with everyday operational decisions. A WAF evaluates HTTP requests and can block many malicious patterns before they reach an application.
This article is based on a real 2025 incident or official security disclosure. Cloudflare reported blocking 20.5 million DDoS attacks in the first quarter of 2025, a 358% year-over-year increase.
The aim is to connect the technology with everyday operational decisions. Unexpected forwarding rules, unfamiliar login locations, messages in Sent that the owner did not create, password-reset emails and sudden delivery problems…
This article is based on a real 2025 incident or official security disclosure. On 9 April 2025 CISA added CVE-2024-53197 and CVE-2024-53150, Linux kernel out-of-bounds vulnerabilities, to its Known Exploited Vulnerabilities…
The aim is to connect the technology with everyday operational decisions. File and directory permissions determine which users and processes may read, modify or execute data.